What Is a Forward Proxy?
A forward proxy sits between users and the internet, deciding what outbound traffic gets through. It overlaps with a firewall in places, but the two do different jobs.
A forward proxy is a gateway for outbound traffic. Users inside a network send their requests through it, and it applies policy: allow, block, log, cache, or inspect. It is not the same as a firewall, and it is not the same as a reverse proxy.
- Forward proxy = client-side gateway. It represents the users and governs what they can reach on the internet.
- Firewall = perimeter filter. It works on both inbound and outbound traffic, usually at the network and port level rather than the application level.
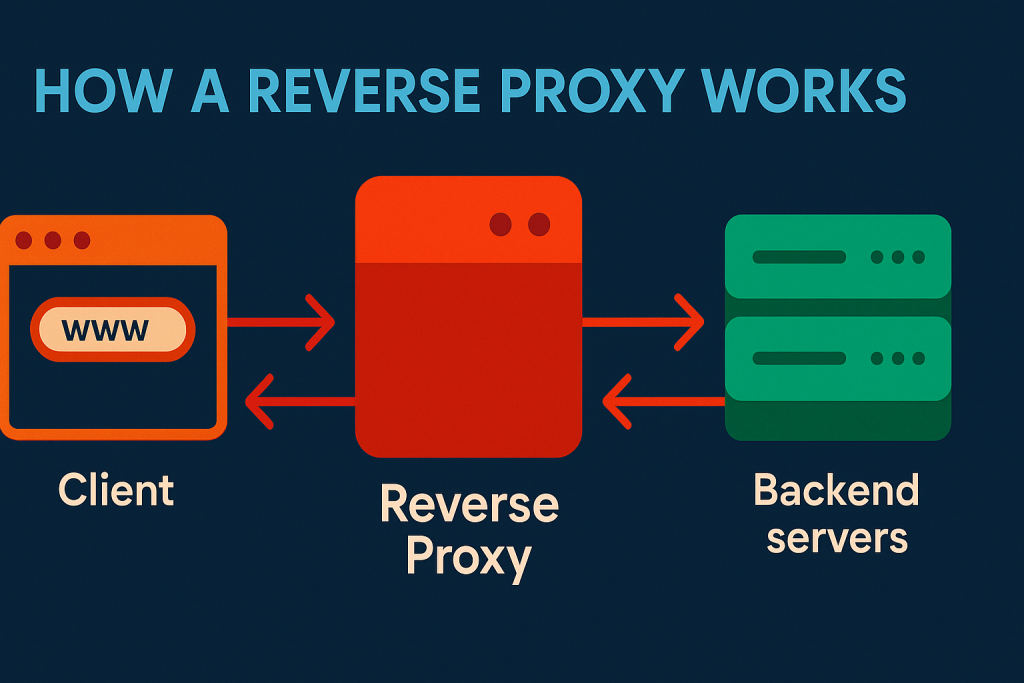
- Reverse proxy = server-side gateway. It sits in front of your own services and manages what comes in from outside.
- In cloud security stacks, forward proxies do the inline SSL inspection and per-user policy enforcement that SASE and zero-trust architectures depend on.
- They have real limits with BYOD, where you can't force a client agent onto every personal device.
A forward proxy intercepts a request from a user inside a network, checks it against policy, and forwards it to the destination on the user's behalf. The destination server sees the proxy's IP address, not the user's. That single indirection is what enables access control, privacy, caching, and threat filtering on outbound traffic.
What a Forward Proxy Actually Does
From a small team to a large enterprise, a forward proxy gives an organization control and visibility over traffic leaving its network. The common functions:
- Access control: allow or block requests based on policy — by category, domain, user, or time.
- Privacy: the destination sees the proxy IP, which hides individual user addresses.
- Caching: frequently requested resources are stored and served locally, cutting load times and bandwidth.
- Threat filtering: combined with threat intelligence feeds, the proxy can block malicious downloads or known bad domains before they reach a user.
Forward Proxy vs Firewall
Both manage traffic, but at different layers and for different reasons. A firewall decides whether a packet is allowed based mostly on addresses and ports. A forward proxy decides based on who is making the request and what they are trying to access.
| Aspect | Forward Proxy | Firewall |
|---|---|---|
| Traffic direction | Primarily outbound (user → internet) | Both inbound and outbound |
| Main audience | Internal users and their sessions | The network perimeter as a whole |
| IP masking | Yes — the destination sees the proxy IP | No, unless NAT is configured |
| Granularity | Application-level (URLs, categories, users) | Usually network- and port-level |
| SSL/TLS inspection | Commonly supported inline | Less common; more resource-intensive |
Where They Overlap
In practice, most organizations run both. The firewall handles broad network-level filtering and known-bad blocking. The forward proxy adds identity-aware, content-aware control on top. Together they cover more ground than either does alone, which matters for scenarios like ransomware containment and insider-threat monitoring.
Forward Proxies in Cloud Security
As traffic moves to SaaS and web apps, and as almost everything runs over HTTPS, traditional inspection at the network layer struggles. A forward proxy operates inline at the application layer, which is where it earns its place in a modern security stack:
- SSL decryption: the proxy terminates and re-establishes TLS so it can inspect encrypted traffic for malware or data leaks, then re-encrypts before forwarding.
- Distributed deployment: geographically spread proxy points-of-presence keep latency low by routing each user to a nearby node.
- Zero-trust enforcement: sitting at the edge, the proxy applies identity-based access rules and per-user behavioral checks on every request.
SASE and CASB
Cloud Access Security Brokers (CASBs), SaaS security platforms, and identity providers frequently use forward-proxy mode to enforce zero-trust policy: block, allow, or inspect a request based on the user, the app, the data involved, and the region it is traveling to.
Using a CASB in Forward Proxy Mode
Running a CASB inline as a forward proxy gives real-time inspection of application traffic: sanctioned SaaS access, contextual policy enforcement, and visibility into what employees are actually using.
- Application discovery: see which SaaS apps are in use, including shadow IT the security team never approved.
- Data classification: tag content by sensitivity so inspection depth scales with risk.
- DLP enforcement: apply controls as specific as blocking uploads of certain file types or preventing account sharing on dev tooling.
A typical rollout: a design team is allowed to sign into approved cloud apps like Dropbox or Notion, while the same policy blocks uploads to unmanaged personal storage.
The BYOD Limitation
Forward proxies work best on managed devices. On BYOD (bring-your-own-device) they hit real constraints:
- You can't require a client agent for full-tunnel routing on a personal device.
- Privacy expectations limit how much visibility you can reasonably have into personal traffic.
- Unmanaged devices carry more risk from ad-hoc plugins and downloads.
When You Want a Reverse Proxy Instead
A forward proxy helps internal clients reach the web safely. A reverse proxy does the opposite: it sits in front of your own backend services and manages traffic coming in from outside. Typical reverse-proxy jobs:
- Caching and load balancing for inbound web traffic.
- Web application firewall (WAF) integration.
- Inspecting inbound payloads such as webhooks and media requests.
- Absorbing traffic spikes and shielding origin servers from DDoS.
Final Thoughts
A forward proxy gives an organization precise control over outbound activity: which apps, which users, which data, inspected or blocked as policy requires. Used alongside a firewall and identity infrastructure, it's a core piece of how SASE and zero-trust architectures actually enforce their rules.
It's not a firewall replacement and not a reverse proxy. Each tool covers a different direction of traffic, and a complete setup usually runs all three.
Frequently Asked Questions
HTTP_PROXY/HTTPS_PROXY/ALL_PROXY environment variables. Authenticate, then verify with a "what is my IP" check that traffic is routing through the proxy. From there you can layer on allow/deny lists, category filters, logging, and caching.