Multi-Account Management
in 2026: Proxies,
Browsers, and Behavior
Running more than one account per platform means passing three independent checks, not one. Here's how the network, browser, and behavioral layers fit together, and where to go deeper on each.
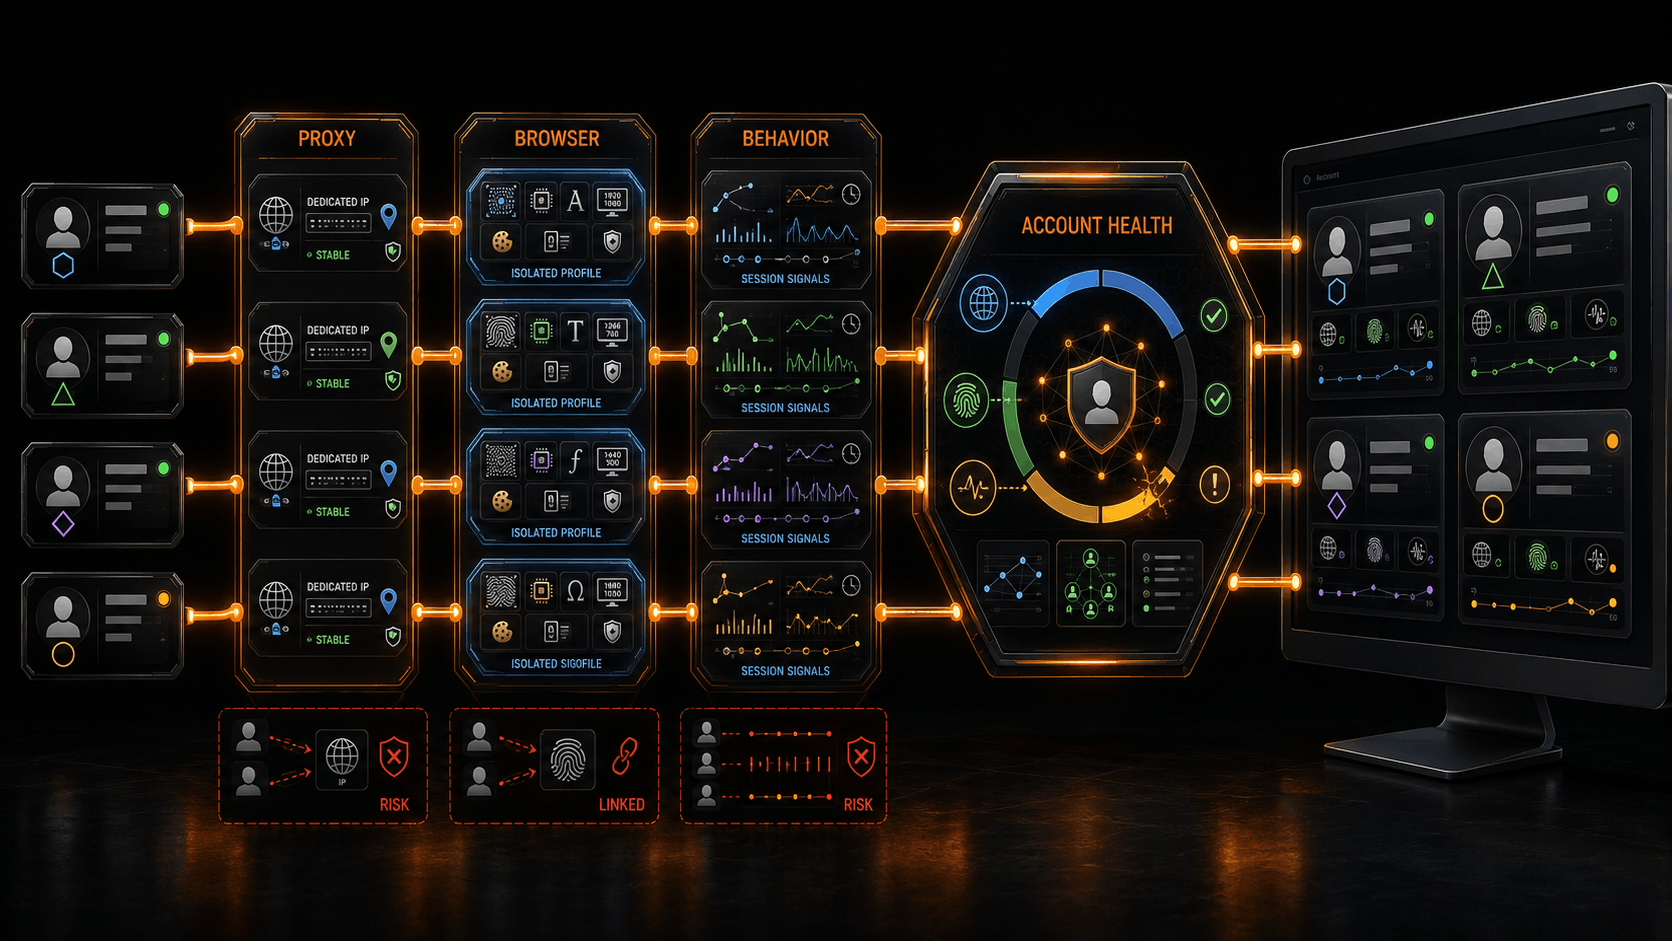
- Multi-account bans rarely trace back to one mistake. Platforms now score three independent layers, network, device, and behavior, and a strong two layers won't cover for a weak third.
- Bots and automated traffic made up 53% of global web traffic in 2026, up from 51% in 2024, and platforms increasingly reuse the same composite-scoring infrastructure to catch linked accounts, not only automation (Thales/Imperva 2026 Bad Bot Report).
- Proxy architecture still decides the network layer. One dedicated IP per account, permanently, is the rule that holds across platforms; sticky-rotating and datacenter IPs fail it in different ways.
- Antidetect browsers have gone mainstream for account isolation. AdsPower alone reports serving over 9 million users worldwide as of April 2026 (AdsPower).
- Behavioral realism is the layer most platforms now weight heaviest, and the one a clean proxy and a stealth browser profile can't fix on their own.
Running a handful of Discord servers, a dozen TikTok accounts, or a client roster of Instagram profiles used to come down to one question: do you have enough proxies. That question still matters, but it stopped being the only one a while ago. Platforms now build a session score out of three layers that operate independently of each other: the network connection, the browser executing the page, and the behavior happening inside it. A session can pass two of the three cleanly and still get flagged on the third.
This guide is the starting point for multi-account management in 2026. It covers what each layer actually checks, where operators most often get the architecture wrong, and which of our deeper technical guides to read next depending on which layer is giving you trouble. If you want the full mechanics of the composite scoring model itself, our complete anti-detection stack guide goes further into the code-level detail than fits here.
Why Multi-Account Management Got Harder in 2026
Detection used to run almost entirely on IP reputation: one flagged IP meant one banned account, you'd buy a new proxy, and move on. That model broke down as platforms folded multi-account detection into the same bot-defense infrastructure built to fight automated traffic at scale. Bots accounted for 53% of global web traffic in 2026, up from 51% in 2024, while AI-driven bot attacks grew 12.5-fold year over year (Thales/Imperva 2026 Bad Bot Report). Every major bot-management vendor responded by combining network, device, and behavioral signals into one composite score rather than checking any single one in isolation, and multi-account detection piggybacks on that same architecture.
The practical effect for anyone running more than one account per platform: your proxy is no longer the whole defense. It's one input into a score that also weighs your browser's fingerprint and how you actually behave once you're logged in. Our companion piece on how platforms build that composite score breaks down each signal layer in detail; the summary here is the version you need to plan a multi-account setup, not build a bot.
Layer One, the Proxy: Getting Your Network Identity Right
The network layer is still the foundation, and it still fails predictably. The rule that holds across LinkedIn, Instagram, TikTok, Telegram, and most other platforms is one dedicated IP per account, permanently, not shared and not rotating. Sticky residential sessions fail that rule because the IP eventually expires and reassigns, creating IP inconsistency the platform reads as suspicious. Datacenter proxies fail it differently: hosting-provider ASNs are an easy signal to flag regardless of how the session behaves otherwise. Our full breakdown of that one rule walks through the platform-by-platform mechanics; this section is the short version.
Which proxy type fits depends on whether the account is meant to last. For accounts you're building a real history on, ISP static proxies are the natural fit: a fixed IP registered to a consumer ISP, starting at $2.30 per IP per month at volume, with unlimited data and no rotation by design. For tasks that need volume across many accounts in a fixed window, like batch signups or sneaker drops, a hybrid rotating pool such as Plan X blends residential, ISP, and mobile sources to reduce subnet-level flagging when one range gets identified. Neither replaces the other; they cover different stages of an account's life. Our hybrid proxies decision guide goes deeper into exactly when the hybrid pool earns its cost over a straight ISP setup.
Layer Two, the Browser: Fingerprints, Profiles, and Isolation
A clean IP doesn't help if every account logs in from the same browser profile. Canvas rendering, WebGL output, installed fonts, and dozens of other JavaScript-readable properties combine into a fingerprint that identifies the device independent of the network connection, and platforms including Meta, Google, LinkedIn, and TikTok correlate that fingerprint across accounts to catch operators running multiple profiles from one Chrome install. That's the layer our dedicated browser fingerprinting guide covers in full; the short version is that the proxy and the browser fingerprint have to be managed as two separate problems, because solving one does nothing for the other.
Two tools solve profile isolation in different ways. Virtual machines give each account a genuinely separate operating environment, at the cost of resource overhead that doesn't scale past a handful of accounts. Antidetect browsers instead generate and persist a distinct, internally consistent fingerprint per profile inside one application, which is why they've become the default for operators running double-digit account counts. Adoption reflects that shift: AdsPower alone states it serves over 9 million users worldwide as of April 2026 (AdsPower). Our virtual machines vs. antidetect browsers comparison covers the tradeoff in more depth, including where VMs still win.
Layer Three, Behavior: The Layer That's Hardest to Fake
This is the layer that decides close calls. A session with a clean IP and a well-isolated browser profile can still fail if the mouse path is too straight, the keystrokes land at suspiciously even intervals, or there's no scroll activity at all before an action fires. Platform documentation from Cloudflare, Akamai, and DataDome describes weighing session realism, mouse trajectory, scroll velocity, keystroke timing, alongside the network and device layers, not as a tiebreaker but as a load-bearing part of the score. Two sessions from the same clean IP and the same browser profile can score differently purely on behavior.
For manual account management, this mostly means avoiding obviously mechanical patterns: identical timing between actions, zero pauses before clicking, navigation that never deviates from the shortest path. For anything semi-automated, it means the automation needs to inject realistic variance rather than assuming a clean proxy and a stealth browser are enough. Our full guide to behavioral bot detection covers the specific signal types and the research behind how reliably they classify human versus automated sessions.
Platform-by-Platform Quick Reference
Detection priorities shift by platform. Here's where each of our platform-specific guides picks up once you've got the three-layer basics down:
| Platform | Primary Risk Signal | Proxy Fit | Deeper Guide |
|---|---|---|---|
| TikTok | Device and region-lock fingerprinting layered on top of IP checks | ISP static | TikTok proxy setup for 2026 |
| Discord | Device and voice-session correlation across servers | ISP static | Managing multiple Discord accounts |
| YouTube / Google | Cross-service tracking shared across the whole Google account graph | ISP static | YouTube channel management proxies |
| Agency / client accounts | Simultaneous logins from one operator across many client profiles | ISP static per client | Managing accounts for multiple clients |
| Sneaker / drop sites | High-volume entries in a fixed time window, batch subnet flagging | Hybrid (Plan X) | Hybrid proxies for multi-account management |
A Simple Framework for Building Your Stack
Most multi-account setups don't fail because the operator picked the wrong proxy. They fail because every account got the same treatment regardless of how much that account was actually worth. A practical way to plan the stack:
- Split accounts into persistent and disposable buckets. An account you're building months of history on needs a different setup than a batch signup you expect to lose.
- Match proxy type to the bucket. ISP static for persistent, long-session accounts; hybrid or rotating residential for volume tasks where individual accounts are expendable.
- Isolate the browser profile per account, not per proxy. A new IP on the same browser profile still links accounts through the fingerprint.
- Put your behavioral effort where the account has the most to lose. A disposable signup batch doesn't need hand-tuned interaction timing; a two-year-old account with a real audience does.
Frequently Asked Questions
Where to Go From Here
Multi-account management in 2026 comes down to three layers that each need their own plan: a proxy architecture that gives every account a stable, dedicated IP; a browser setup that keeps each account's fingerprint genuinely separate; and interaction behavior realistic enough not to undo the first two. None of the three covers for the others.
If you know which layer is causing your problems, go straight to the deep dive: proxy architecture, browser fingerprinting, or behavioral scoring. If you're still setting up the network layer, our ISP proxies start at $2.30 per IP per month with a free 1GB trial to test against your own accounts first.