What Is a Reverse Proxy?
A reverse proxy sits in front of your backend servers and handles incoming traffic — routing it, filtering it, caching responses, and taking the TLS load off the origin.
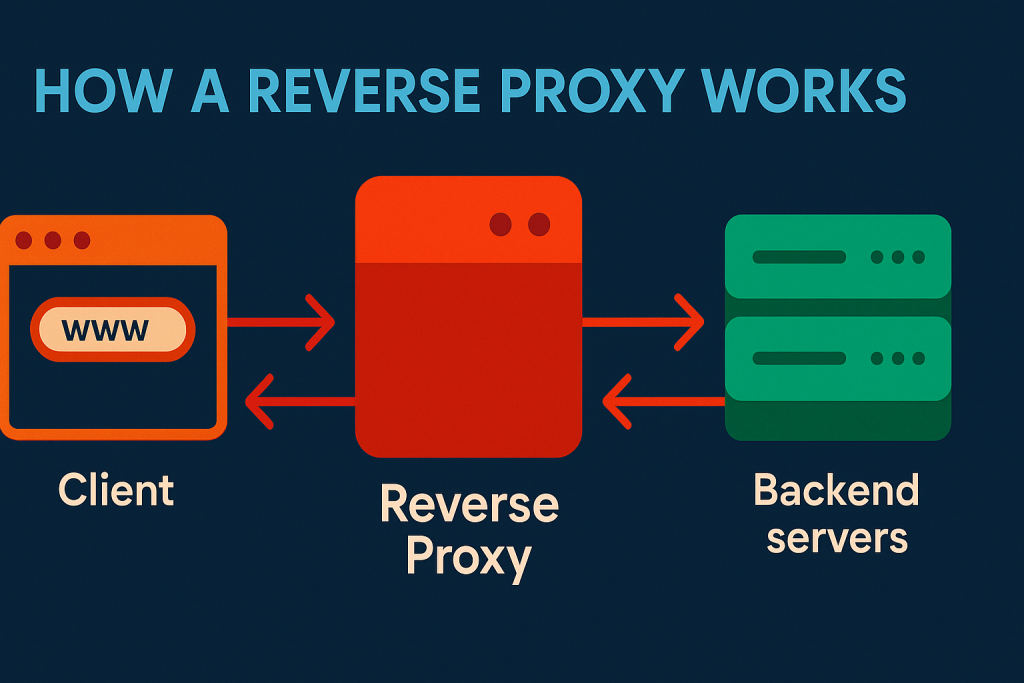
A reverse proxy is a server that stands in front of one or more backend servers. Clients connect to it instead of the origin. It distributes load, screens for threats, caches responses, and handles SSL — without exposing the servers behind it.
- It works on behalf of the server, not the client. A forward proxy does the opposite.
- Load balancing: spreads incoming requests across healthy backends and reroutes around failures.
- Security: hides origin IPs and ports, absorbs DDoS, and centralizes rules like rate limiting and WAF filtering.
- SSL offloading: terminates TLS at the proxy so backend servers don't carry the handshake cost.
- Caching: serves repeated requests for static or semi-static content without hitting the origin.
When you visit a website protected by a reverse proxy, your browser never talks to the machine that actually holds the site. It talks to the proxy. The proxy decides which backend server should handle the request, fetches the response, and returns it to you as if it were the origin. That indirection is what makes load balancing, caching, SSL offloading, and edge security possible at scale.
What Is a Proxy Server?
A proxy server is an intermediary between a client device and a target server. When a request is made, the proxy intercepts it and either forwards it to the destination or blocks it, based on policy.
Forward vs Reverse
- Forward proxy: sits in front of clients. Used by people or teams to reach external sites — it protects and represents the client. See what a forward proxy is and how it compares to a firewall.
- Reverse proxy: sits in front of servers. It shields internal infrastructure from direct client access — it protects and represents the server.
What Proxy Servers Give You
- Privacy: masks IP addresses on whichever side the proxy represents.
- Control: applies filtering and monitoring policy, such as blocking restricted content.
- Security: screens traffic for threats before it reaches the protected side.
Firewalls, VPNs, secure web gateways, and content delivery networks all build on proxy technology underneath.
How a Reverse Proxy Works
A reverse proxy sits between the end user and your backend servers. When someone loads your site:
- The client's browser sends a request to your domain.
- The reverse proxy receives it — not the web server.
- The proxy picks the best backend server to handle the request (by health, load, or region).
- It fetches the response and returns it to the client, appearing as the origin.
Key Points
- IP concealment: clients never see internal server addresses, which reduces the attack surface.
- Session handling: the proxy keeps continuity between a user's requests and the backend serving them.
Unlike a forward proxy, the reverse model acts for your application rather than for the people using it. It protects servers, not users.
Key Benefits of a Reverse Proxy
1. Load Balancing
The proxy distributes incoming traffic across multiple servers, which:
- Prevents any single server from being overloaded.
- Keeps the application available through traffic spikes.
- Maintains responsiveness regardless of volume.
For a site handling thousands of requests per second, the proxy checks backend health and reroutes traffic away from an unhealthy node within seconds.
2. Security
This is where services like Cloudflare earn their keep. A reverse proxy can:
- Block malicious IPs before they reach core servers.
- Rate-limit abusive traffic to blunt DDoS attacks.
- Hide backend IP and port combinations from attackers.
- Enforce security rules centrally at the proxy layer instead of per-server.
3. SSL Offloading
Terminating TLS for high volumes of HTTPS traffic is expensive. The reverse proxy takes on that handshake work:
- Decrypts inbound TLS and manages certificate negotiation.
- Delivers edge-level performance for the client connection.
- Frees backend application servers from encryption overhead.
4. Caching
By caching static assets and stable dynamic content, the proxy cuts how often the backend is hit, which improves:
- Page load speed.
- Server load.
- Content delivery time.
If a thousand users request an unchanged homepage banner, a cached copy serves them all without regenerating anything.
5. Global Server Load Balancing
For organizations serving users worldwide, the proxy routes visitors based on:
- Geographic location.
- Current capacity at each data center.
- Failover to another region during an outage.
The result is faster connections and cleaner recovery when a region goes down.
Reverse Proxy vs Forward Proxy
| Feature | Forward Proxy | Reverse Proxy |
|---|---|---|
| Stands in for | The client | The server |
| Used by | Individuals or teams needing access | Teams running backend services |
| Traffic direction | Outbound (to the internet) | Inbound (from the internet) |
| Typical purpose | Bypass geoblocks, hide users, filter content | Security, load distribution, SSL offload |
An analogy: a forward proxy is like a VPN on employee devices, controlling how they reach out. A reverse proxy is the managed front door to an e-commerce platform's product servers, controlling how customers get in.
How to Implement a Reverse Proxy
- Choose a solution: NGINX, Apache with
mod_proxy, HAProxy, or a DNS-based option such as a CDN (Cloudflare, Fastly). - Define your backends: list the upstream applications that need to be reachable.
- Configure routing: map which incoming paths and hostnames go to which backend.
- Install SSL certificates at the proxy layer, wildcard certs included, so TLS terminates there.
For a hands-on walkthrough, JayMartMedia's NGINX reverse proxy guide covers a basic setup step by step. CDN-based options handle most of this for you, which suits e-commerce stores, B2B apps, and microservice startups.
What Is a Reverse Proxy Used For?
- High-traffic web portals: shopping sites, media platforms, banking systems.
- APIs that need rate limiting and persistent authentication handling.
- Mobile app backends with multi-region cloud services under peak load.
- Microservice architectures that route requests through a secure API gateway.
Final Thoughts
Modern sites and APIs aren't designed to expose their servers directly to the open web. A reverse proxy adds a controlled layer in front — routing traffic, absorbing attacks, caching responses, and terminating TLS — so the origin stays hidden and the user-facing experience stays fast.
If uptime and performance under load matter to your product, a reverse proxy is usually one of the first pieces of infrastructure worth putting in place.